New AI bill of materials and MCP security

secure the code AI writes.
and the code that calls AI.

Code security for teams shipping with AI.

Inventory every AI provider, model, agent and MCP server in your repositories. Trace where untrusted input reaches a prompt and where model output reaches something dangerous. Keep code scans, dependencies and pull request reviews in one workspace.

Free plan available · No credit card required

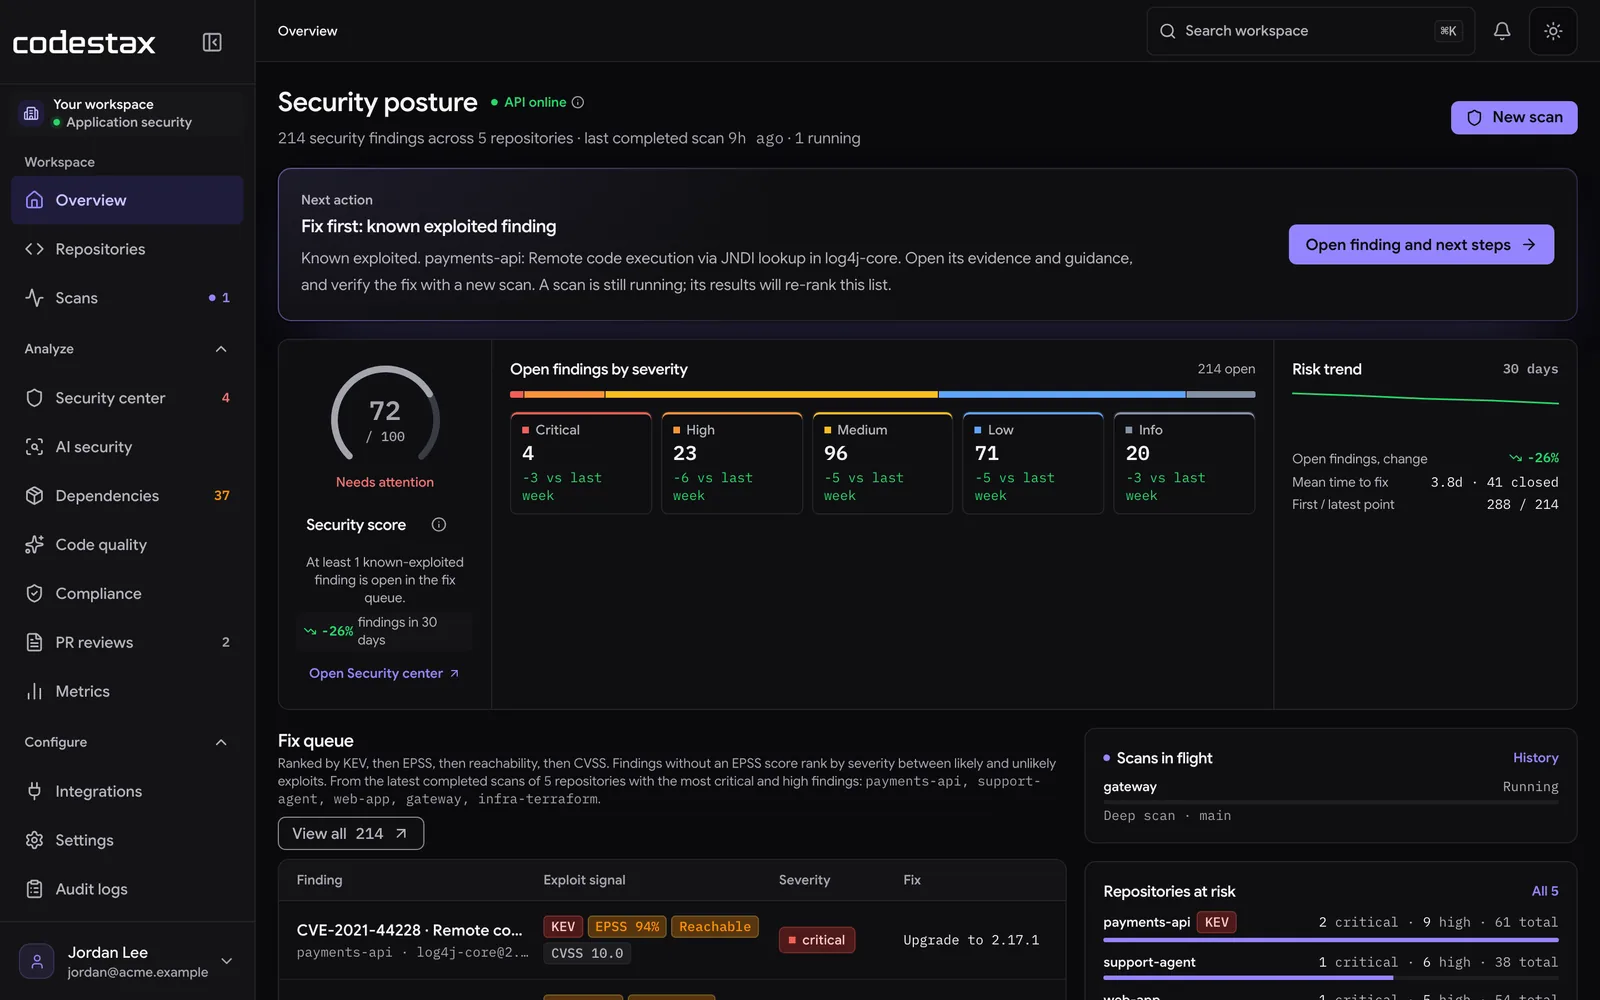
The CodeStax Overview: security score 72, open findings by severity, and a fix queue that ranks a known-exploited log4j-core vulnerability first.
Product screenshot · sample data

Integrates with your workflow

  • GitHub
  • Bitbucket
  • GitLab
Your repositories. Your workflow.

01 / The workspace

from finding to next action

Follow an example from scanner evidence to a proposed change and the checks needed before closing it.

01

See every model, agent and MCP server.

AI attack surface management inventories the AI your code calls and traces untrusted input into prompts and model output into tools, shells and queries.

An AI bill of materials for every repository.Explore this capability
codestax.co/dashboard

AI inventory - api-server

AI-BOM
Agentsupport-assistant

Model output reaches a shell command

agent/run.ts:41
Critical
MCP serverfilesystem-tools

Write access outside the workspace

.mcp/config.json
High
Model callchat completion client

Request body reaches the system prompt

lib/llm.ts:18
High

Product preview · illustrative sample data

scan engines
6
One coordinated scan
source providers
3
GitHub, Bitbucket, and GitLab
starting price
$0
No credit card required
day Growth trial
14
For organization workspaces

02 / Connected coverage

complete code security

From the code you write to the packages, infrastructure, and AI systems it depends on.

AI attack surface management

AI is part of your stack.
Make it part of your
security picture.

Inventory models, agents, tools, prompts, and MCP servers. Trace how untrusted input reaches them and where their output goes, then review the risks in context.

AI security and AI-BOM
Explore all features

03 / From commit to confidence

fits your workflow.
moves your team forward.

01

Connect

Import repositories from GitHub, Bitbucket, and GitLab through a configured provider connection.

02

Scan

Run coordinated analysis. Review findings with severity, code context, and prioritization signals.

03

Ship

Bring remediation into pull requests and enforce the quality gates your team configures.

CodeStax / security pipeline01 → 03
One commit. Full context.api-server / main · a8f32c1
SAST
SCA
Secrets
IaC
Container
AI attack surface
Context meets code.
14+ { role: "user", content: user_input }
Untrusted input kept out of the system promptTraced from request to model call. Pair with a tool allowlist.
Illustrative workflow · SAST, SCA, secrets, IaC, container and AI attack surfaceStatic preview

How we compare

Find the right fit for your security and code review workflow.

Compare platforms

04 / Per-seat pricing

start free, then
pay per seat.

Start with your first repository. Add the capacity your team needs, with transparent annual pricing.

Free

Free

No credit card required

  • 1 developer
  • 1 repository
  • 5 scans/month
  • 3 AI PR reviews/month
Get started free

Pro

$22/seat/mo

Billed annually. Save 24%.

  • Unlimited repos
  • Unlimited scans
  • Review velocity + audit export
  • Priority support
Choose Pro (Pro plan)

Enterprise

Custom

Volume pricing and custom terms.

  • Volume pricing
  • Compliance reports
  • Priority onboarding
  • Dedicated CSM
Talk to sales

Organization workspaces start on a 14-day Growth trial with no card needed. Personal workspaces start on Free.

Compare all plan limits

05 / Your next commit starts here

ready to secure
your code?

Give your team the context to ship with confidence.